Domain Name System (DNS), the system that translates domain names into IP addresses, is one of the most foundational parts of the internet. It’s also one of the least inspected by traditional security tools.
Now, attackers are taking advantage of this oversight to use it as a cover channel to deliver malware.
A recent Ars Technica article uncovered a sophisticated campaign where hackers embedded malware inside DNS TXT records. These records, typically used for harmless tasks like domain verification or email authentication, were repurposed to store chunks of malicious code.
In this campaign, malware was first converted into hexadecimal format and split into hundreds of small chunks. The attackers then registered a domain, whitetreecollective[.]com, and created hundreds of subdomains. Each chunk of malware was then stored in the TXT record of one of the subdomains.
Once an attacker gains access to a network, the malware could be reassembled by making a series of DNS requests to these subdomains. Since DNS request traffic is both routine and rarely inspected, this method would allow the attackers to bypass traditional security tools.
DNS has often been used for covert channels and data exfiltration via tunneling, but hosting full malware payloads in DNS records is a more brazen and novel tactic. It underlines the need for DNS-level visibility and enforcement as part of a modern enterprise security strategy.
Versa DNS Security: a purpose-built solution for DNS-based threats
Versa’s approach to DNS security is designed to detect these kinds of evolving attacks. Part of Versa Unified SASE and delivered through its Secure Web Gateway (SWG), Versa DNS Security is a fully integrated, cloud-delivered service that combines DNS filtering, reputation analysis, behavioral detection, and integration with broader security layers.
Specifically, Versa’s DNS Security works across multiple dimensions to:
- Filter DNS queries based on type, size, and frequency.
- Evaluate domain reputation in real time.
- Detect tunneling behavior and encoded data patterns.
- Integrate with URL filtering, advanced file filtering, and IPS to block threats outside of DNS.
This layered approach ensures that threats hiding in DNS traffic are identified and stopped as early as possible.
How Versa neutralizes the attack techniques described
Let’s take a closer look at how Versa can directly address the tactics used in this and similar DNS-based attacks.
1. Detecting DNS records hosting malware and malicious scripts
Attackers using DNS records to host malware and malicious scripts is not a new behavior, and Versa is well-versed in detecting and stopping these threats. Versa’s multiple security layers work together to prevent the use of DNS records for attacks through a combination of reputation and behavioral analysis:
- IP and domain reputation: If a DNS response contains an IP address known for hosting malware, Versa’s reputation-based IP filtering will block subsequent traffic to that IP. Even if a device is compromised or a DNS cache is poisoned, Versa will prevent the connection to suspicious or malicious command-and-control servers.
- DNS sinkholing: For domains identified as suspicious or malicious, Versa can use a DNS sinkhole action to prevent compromised devices from connecting to command-and-control servers. Rather than allowing the client to connect to the actual IP address returned in a DNS response, the request is redirected to a safe or internal IP address. This allows security teams to collect forensics information about an attack while keeping users and resources safe.
- Integration with advanced filtering: Versa’s DNS filtering integrates with Versa Intrusion Prevention System (IPS) and advanced file filtering to identify threats using signature-based and anomaly detection to protect against malware delivered via DNS.
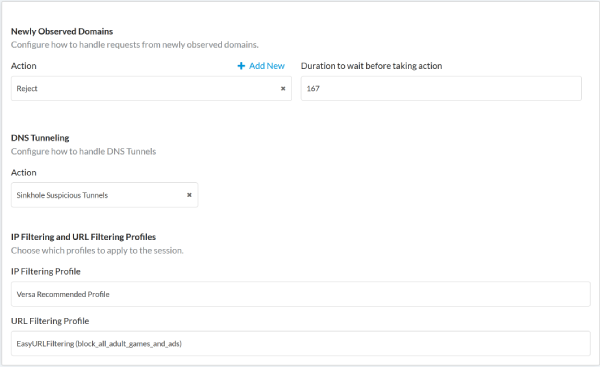
2. Detecting hidden and encoded threats hosted in DNS records
In the Ars Technica article, instead of directly hosting malware in the DNS TXT field, the attackers added a new layer of subterfuge by encoding the malware file into hexadecimal format and breaking it up into chunks. Attackers often use TXT records to hide payloads because these records can store arbitrary text.
While Versa doesn’t inspect every TXT record’s content directly, it provides powerful controls to block risky requests:
- Query-based controls allow administrators to limit or block large TXT records or suspicious query volumes, which are commonly used in DNS amplification and data exfiltration. This is especially useful in defending against attacks like this one where the payload is delivered in segments via multiple TXT responses.
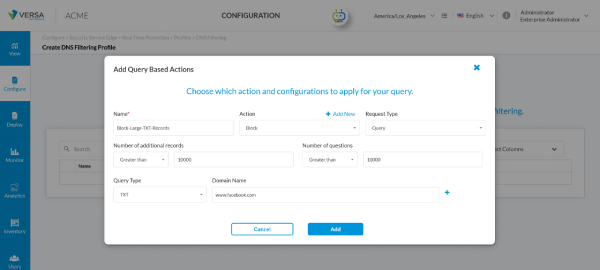
- Reputation-based blocking ensures that any queries to a known suspicious/malicious domain, or newly registered domains without a reputation, are automatically blocked. In the attack above, Versa can block the queries to the newly created subdomains (on whitetreecollective[.]com in this case) containing the encoded malware chunks since they did not have reputations. This allows Versa to mitigate zero-day attacks like the one described.
This means that even if malware is encoded and hidden inside a TXT record, Versa can prevent the malware from infecting the victim network.
3. Detecting attempts to contact command-and-control (CnC) servers
DNS tunneling is a technique that hides data or communication inside DNS queries and responses to bypass security and/or exfiltrate information from a network. In the article, the attackers attempted to use DNS tunneling to transfer malware from a command-and-control (CnC) server (whitetreecollective[.]com) into a network.
The behavior observed – frequent, repetitive requests to a single domain or its subdomains – is one characteristic of DNS tunneling.
Versa DNS Security is specifically designed to detect DNS tunneling and block CnC server communication through:
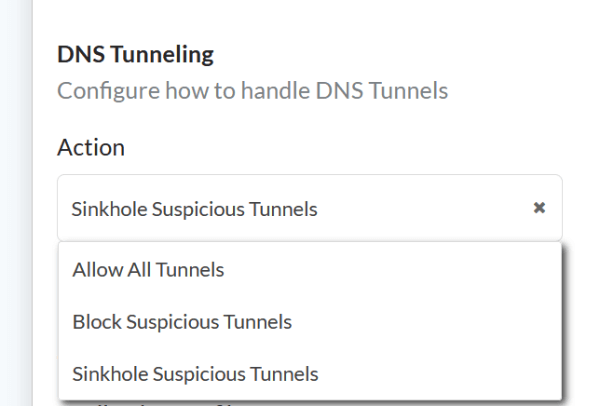
- DNS tunneling detection: Versa’s DNS Tunneling detection can identify malicious activity using frequency-based detection and invalid character detection. The former can track repetitive and uncommon requests over a period of time to block requests once limits are exceeded while the latter inspects DNS queries for invalid characters, an indicator of encoded data within DNS traffic.
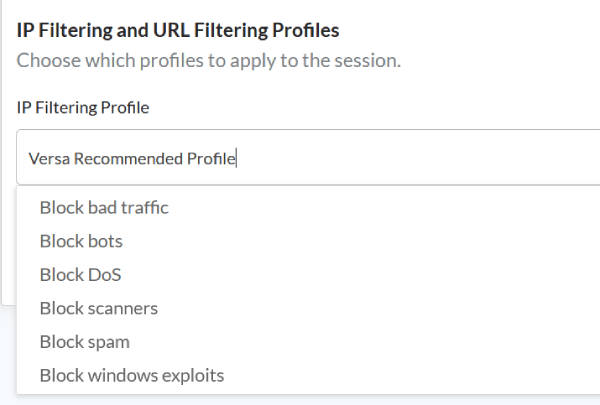
- URL filtering integration: Versa DNS works in conjunction with other Versa security functions including IP and URL Filtering. Even if a malicious DNS query is resolved, subsequent HTTP/HTTPS traffic would be inspected and blocked by URL filtering based on categorization and threat intelligence.
Versa is highly effective at detecting these and other sophisticated security threats. To see how Versa performs in real-world threat detection, check out the CyberRatings.org 2025 Comparative Test Report: Security Service Edge (SSE).
Attackers will continue to exploit overlooked infrastructure like DNS to deliver malware and exfiltrate data. Versa’s multi-layered protections form a robust defense against sophisticated DNS-based attacks.
By applying real-time inspection, behavioral analytics, and integrated filtering, Versa DNS Security can identify, block, and neutralize threats well before they reach the user or the network.
To learn how Versa’s DNS Security and other Security Service Edge products can help protect your organization from these and other novel attacks, schedule a demo with our team today.
Shubham Sangle is a product manager working across Versa's Security Service Edge portfolio, including DNS security, Secure Enterprise Browser, and AI-enhanced data loss prevention. He writes frequently on emerging attack techniques.